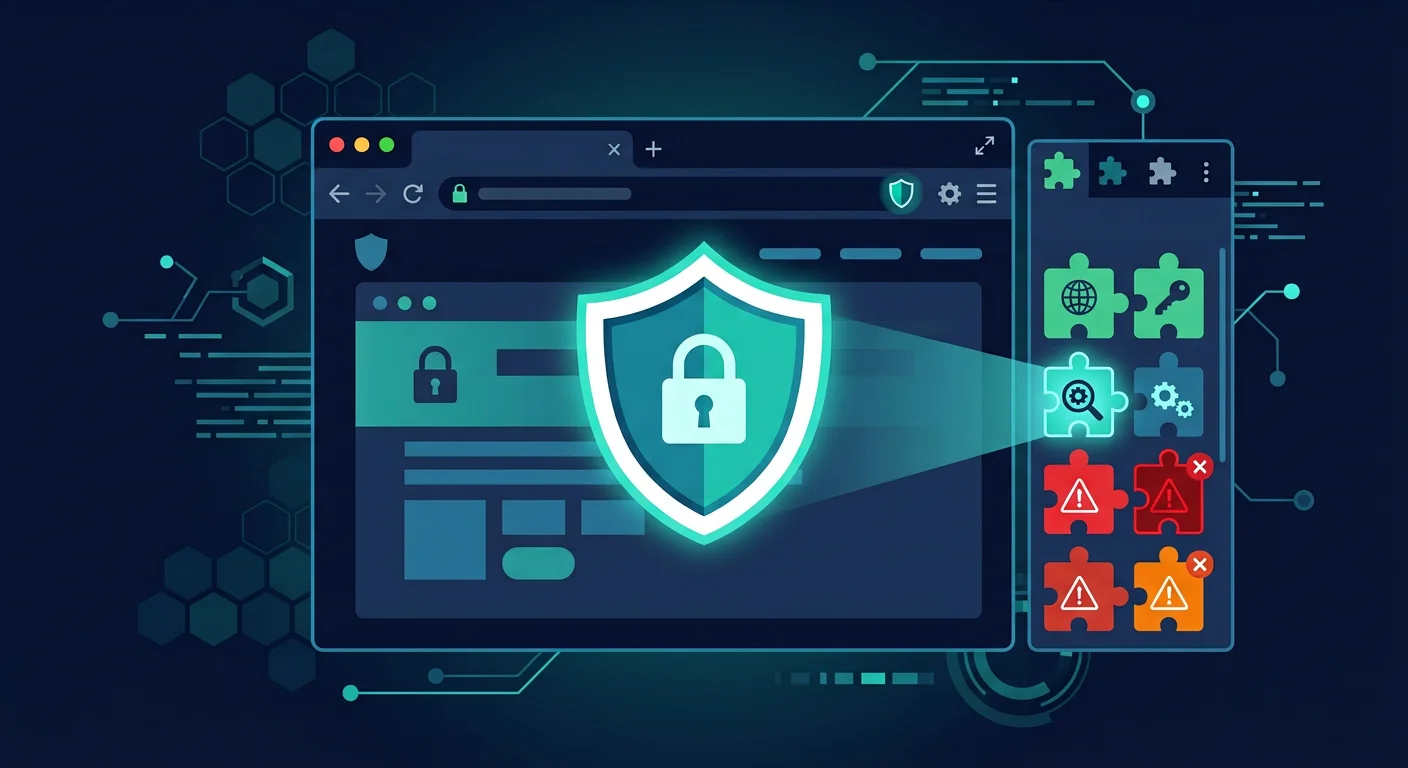
Your browser stores more information about you than you might realize: browsing history, saved passwords, tracking cookies, form data, site permissions, and a list of extensions that can read every page you open. Extensions themselves request broad access: "read and change all data on all websites." The combination of an unconfigured browser and unchecked extensions creates a large risk profile.
Why browsers are the primary target
The browser is the point where all your online activities converge. Banking, email, shopping, social media, work: everything passes through the browser. Attackers know this and target browsers through several vectors: malicious extensions, sites exploiting browser vulnerabilities, malicious ads (malvertising), and man-in-the-browser attacks. Extensions are especially attractive to attackers because they operate with high permissions. A popular ad-blocking extension can be sold to a new owner who injects tracking code without users' knowledge. This has happened multiple times.
8 steps to secure your browser
1. Choose a privacy-focused browser
Not all browsers treat security and privacy equally. Firefox and Brave have stronger built-in tracking protections than default Chrome. If you use Chrome, tighten its settings. Whatever your choice, make sure the browser is always updated to the latest version.
2. Tighten built-in privacy settings
Open your browser settings and review the privacy section:
- Third-party cookies: Block or restrict
- Do Not Track: Enable
- Cross-site tracking: Block if available
- JavaScript for unknown sites: Consider restricting
- Notifications: Disable default notification permissions These changes reduce the number of trackers that can follow you across sites.
3. Audit every installed extension
Open your browser's extension page. For each installed extension, ask:
- Am I still using it?
- Who is the developer? Are they trustworthy?
- What permissions does it request? Do they make sense for its function?
- When was it last updated? Remove extensions you do not use, whose developers are unclear, or that request excessive permissions. A calculator extension does not need to read data on all websites.
4. Be cautious before installing new extensions
Before installing an extension, even from the official store, check:
- User count and reviews: Extensions with many users and positive reviews are safer, but not a guarantee.
- Developer: Research whether the developer has a reputation. Extensions from established companies (like Bitwarden, uBlock Origin) are generally more trustworthy.
- Requested permissions: Compare with the functionality. If it does not make sense, do not install.
- Privacy policy: Read the extension's privacy policy. Note whether they collect data and for what purpose.
5. Use proven security extensions
Some extensions add defensive layers without much risk:
- uBlock Origin: Efficient and open-source ad and tracker blocker
- Bitwarden: Open-source password manager
- HTTPS Everywhere: Forces HTTPS connections (now built into most modern browsers) Install only what you need. Every additional extension adds attack surface.
6. Clean browser data periodically
Browsing history, cache, cookies, and site data accumulate over time. Clean them at least monthly, especially third-party cookies and data from sites you no longer visit. Some browsers offer automatic cleanup on close.
7. Use separate browser profiles
Separate sensitive activities (banking, work email) from casual ones (social media, shopping). Create separate browser profiles for each context. If one profile is compromised, the other remains isolated. Firefox Multi-Account Containers or Chrome Profiles can serve this purpose.
8. Review site permissions periodically
Browsers store permissions you have granted to sites: location, camera, microphone, notifications, clipboard. Open site permission settings and revoke unnecessary permissions. Many sites request notification permissions that are later used to send spam or fake alerts.
Example: popular extension sold to malicious party
A Chrome extension with millions of users suddenly received an update with new code. The original developer sold the extension to a company that injected tracking scripts. Users received no notification about the ownership change. The new script collected browsing data and sent it to the buyer's servers. Thousands of users were affected before the security community discovered the code changes. This shows that even "trusted" extensions can become threats when ownership changes hands.
Common browser user mistakes
- Storing all passwords in the browser without additional protection. If someone gains access to your device, they can export all your passwords. Use a separate password manager.
- Ignoring SSL certificate warnings. If your browser warns about an invalid certificate, do not proceed. This could indicate a man-in-the-middle attack.
- Staying logged in on all sites. Log out of banking and email accounts when finished, especially on shared devices.
Frequently asked questions
Does incognito mode protect privacy?
Incognito mode only prevents the browser from storing local history. Your ISP, network administrator, and visited sites can still see your activity.
Are all extensions in the Chrome Web Store safe?
No. Google reviews extensions, but the review is not perfect. Malicious extensions can slip through, especially new ones or those whose ownership has changed.
Do I need a dedicated browser for banking?
Using a separate profile or browser for banking adds an isolation layer. If your main browser is compromised, banking sessions in a separate browser are safer.
Sources and further reading
- EFF: Cover Your Tracks
- Mozilla Support: Firefox Enhanced Tracking Protection
- Chrome for Developers: Permission Warnings
Editorial note: This article is educational and does not recommend specific products. Evaluate your needs and choose tools appropriate to the risk level you face.